You spent an afternoon adding a sleek security widget to your contact page or sign-up form. When you open the page in your browser, a neat little box appears, checks off a green shield, and tells you the visitor is verified. Yet when you check your email inbox the next morning, you find forty junk messages from automated spammers. You check your user database, and there are dozens of fake accounts registered with random strings of letters. If the bot protection is visibly running on your screen, how are automated scripts still walking straight through your front door?
The Front-End Illusion: What Most Teams Get Wrong
This problem happens far more often than engineering teams like to admit. It happens to small independent blogs, busy online storefronts, and even well-funded SaaS startups.
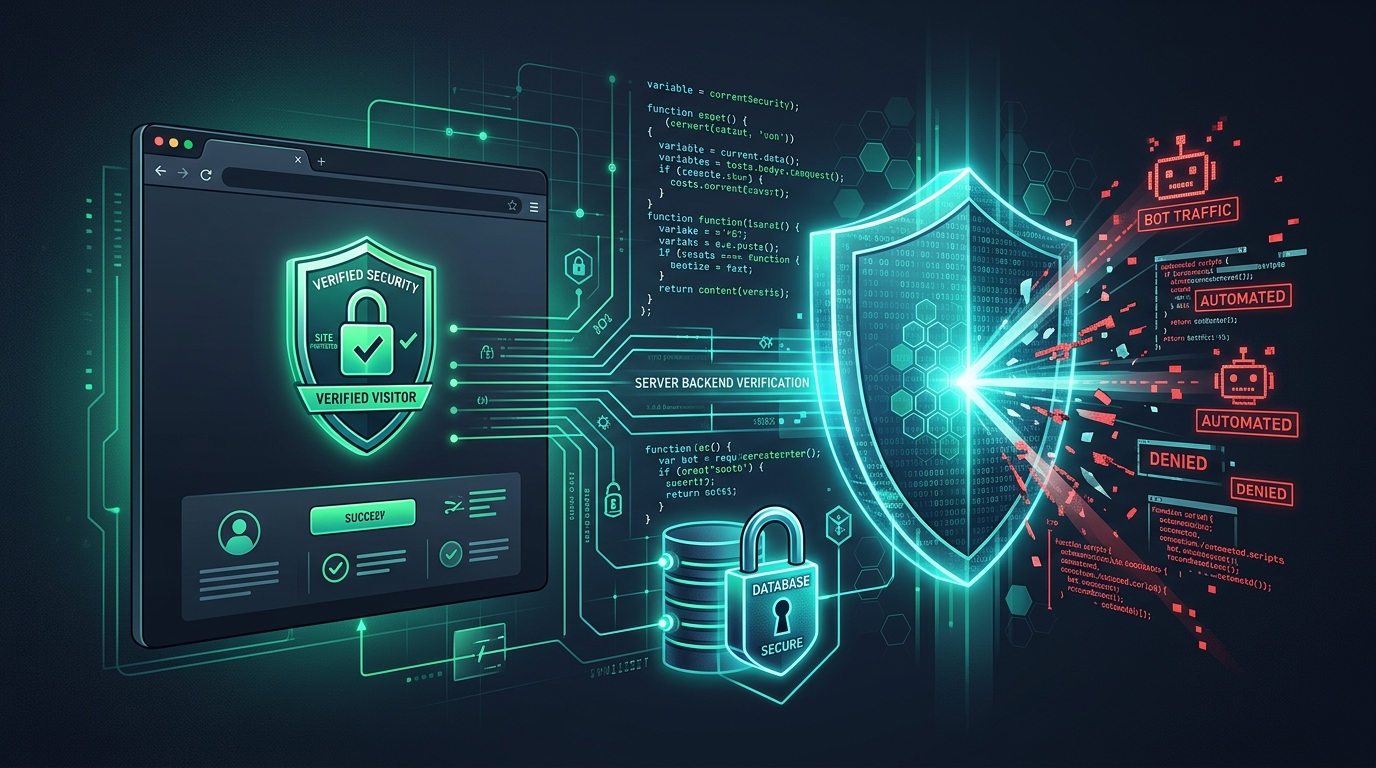
The core issue boils down to a misunderstanding of how bot detection actually works. Most teams complete Step 1 (the visual part in the browser), but completely skip Step 2 (the invisible verification on the server).
The downstream impact of unverified forms quickly cascades into your back-office systems. If a lead capture form or newsletter signup feeds directly into Zapier, your CRM, or an email list, automated bots will burn through your API quotas and flood your team with junk. In our analysis of business automations that actually save time versus ones that drain it, we noted that automated pipelines only remain valuable if the data entering them is filtered and clean at the front door.
When you add a service like Cloudflare Turnstile, Google reCAPTCHA, or hCaptcha to your website, here is what is supposed to happen:
- In the browser: A script runs in the user's browser, evaluates subtle signals (like mouse movement, device characteristics, and browser headers), and generates a temporary encrypted string called a response token.
- During form submission: When the user clicks "Submit," the browser packages up that response token and sends it along with the rest of the form fields to your server.
- On the server (the missing step): Your backend server receives the token, pauses the submission, and sends a private behind-the-scenes message to the security provider’s API to ask: "Hey, is this token genuine and valid for this specific domain?"
- The verdict: Only if the security provider replies with
success: truedoes your backend save the user, charge the card, or send the email.
The Critical Breakdown
When developers only copy-paste the HTML snippet into their frontend template, the widget renders perfectly for real humans. But if the backend code never checks the token against the verification API, the widget is purely decorative. Attackers do not use web browsers; they write Python or curl scripts that send raw HTTP POST requests straight to your API endpoint, ignoring your frontend code entirely.
The 2-Minute Curl Test: Check Your Site Right Now
You do not need specialized cybersecurity software to test whether your website has this vulnerability. You can verify it right from your computer's terminal using a simple command line tool:
Watch what happens when you press Enter:
- If your backend returns
200 OKor sends an email: Your site is completely unprotected. Your backend processed the form without asking for proof that the visitor passed the bot check. - If your backend returns
422 Unprocessable Entityor403 Forbidden: Your backend correctly rejected the submission because the required security token was missing.
Code Comparison: The Flaw vs The Fix
To see why this happens, look at how typical backend code handles incoming form submissions.
The Broken Backend (What Most People Write)
In this all-too-common example, the backend validates standard fields like name and email, but ignores the security token entirely:
The Secure Backend (How It Should Work)
In a properly protected setup, the backend takes the token submitted by the form, queries the verification service using a secret server-side key, and rejects any request that fails the check:
Enter Cloudflare Turnstile Spin: Fixing the Setup Gap
Knowing that thousands of websites suffer from incomplete installations, Cloudflare introduced Turnstile Spin on September 25.
Rather than expecting developers to read twenty pages of API documentation, manage private secret keys manually, and write repetitive HTTP verification code across dozens of controllers, Turnstile Spin is designed to pair directly with modern AI coding assistants and CLI agents (like Claude Code, Cursor, Copilot, and terminal agents).
| Implementation Method | Frontend Widget | Backend Validation | Risk of Bypass |
|---|---|---|---|
| Manual Copy-Paste (Common) | Installed | Frequently Missing (0% protection) | Critical: Bots bypass completely |
| Custom Manual Coding | Installed | Depends on developer diligence | Moderate: Easy to miss endpoints |
| Turnstile Spin with AI Coding Agents | Installed & Wired | Automated end-to-end verification | Minimal: Fully verified token loop |
How Turnstile Spin Actually Works
When you run Turnstile Spin in your project repository alongside an AI coding assistant, it takes a full-stack approach:
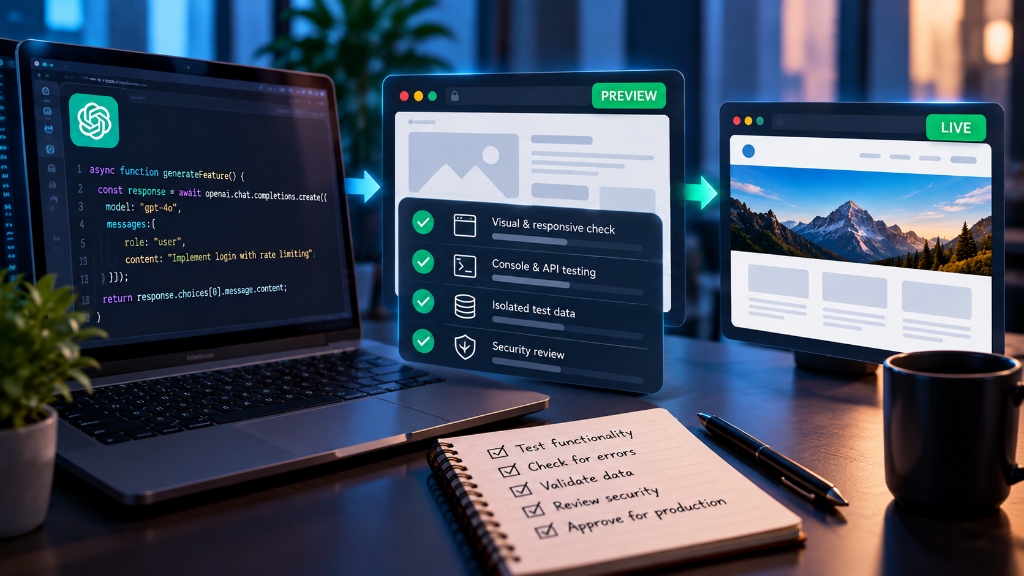
- Repository Code Audit: The tool scans your project routes and form handlers to flag public endpoints accepting submissions without verification. When letting AI coding assistants patch these controllers, you should always test the generated middleware in an isolated branch environment first. Following our framework on testing AI-generated code safely before release, preview deployments let you run terminal curl tests against your patched routes to verify they block bots without locking out real customers.
- Gap Detection: It highlights forms that render the widget in HTML but lack corresponding verification logic on the receiving controller.
- Native Code Generation: Instead of imposing an awkward third-party library, it writes clean, idiomatic verification code for your specific framework—whether that is Laravel, Next.js, Django, Node.js/Express, or Ruby on Rails.
- Environment Secret Management: It ensures your private secret key is placed securely in
.envfiles rather than hardcoded into public repositories or frontend JavaScript bundles.
"Security features that are easy to misconfigure are not truly secure. Automated tools that inspect both the browser and the server close the gap between having the appearance of safety and actual protection."
Honest Limitations: What Bot Protection Does Not Fix
While fixing backend verification stops standard automated form spam in its tracks, no single tool can solve every kind of web abuse. It is vital to understand what Turnstile Spin and challenge widgets can and cannot do:
1. Human "Click Farms" and CAPTCHA Solving Services
There are commercial services where real humans are paid fractions of a cent to manually solve challenges. Because a real human is sitting at a browser clicking the screen, their browser generates a completely legitimate token. Bot protection tests for automated behavior; it cannot know whether a human submission has malicious intent.
2. Shadow and Legacy API Endpoints
If you protect /contact, but forget that an old /api/v1/lead-submit endpoint from two years ago is still active and unmonitored, scrapers will find it. Automated tools can only protect the routes they are instructed to audit.
3. Public Web Scraping of Static Content
Challenge widgets are designed for forms and actions (POST requests). They do not prevent scrapers from fetching public blog posts, product pricing, or directory listings via standard GET requests. Stopping scrapers requires edge-level WAF rules and rate limiting.
A Practical 4-Step Checklist for Your Team
Before you close this tab, here are four steps you can take today to ensure your forms are genuinely protected:
Step 1: Run the Curl Test on Every Public Form
Open your terminal and send an HTTP POST request to your contact or registration endpoint without any security token. If your server accepts the data and responds with success, your backend is missing verification.
Step 2: Never Expose Your Secret Key to the Client
Ensure your Site Key (public) is in your HTML and your Secret Key (private) stays exclusively on your server in an environment variable. If your secret key is leaked in frontend JavaScript, anyone can fake valid responses.
Step 3: Combine Bot Checks with Rate Limiting
Pair your challenge verification with server-side rate limits (e.g., maximum 5 submissions per IP address per hour on contact forms). This prevents brute-force attempts from overwhelming your verification quota.
Step 4: Use AI Coding Agents to Audit Existing Repositories
Take advantage of tools like Cloudflare Turnstile Spin with your coding assistant to systematically inspect your controllers and ensure no public form was left unprotected.
Frequently Asked Questions
Key clarifications and practical answers addressed by The Indox editorial board.
Does Cloudflare Turnstile slow down my form submissions?
No. The client-side challenge runs in the background while the user is typing their message. The backend verification call to Cloudflare’s API typically takes under 80 milliseconds, which is completely imperceptible to a human submitting a form.
Why do developers forget the backend verification step so often?
Because web development tutorials and quick-start guides often show how to embed the widget in HTML as the hero example, while burying the server-side verification code in separate API documentation. Seeing the visual widget work in the browser creates a false sense of completion.
Can I use Turnstile on non-Cloudflare hosted sites?
Yes. Cloudflare Turnstile is a standalone product. You can use it on any website, regardless of whether your DNS or hosting is with Cloudflare, AWS, DigitalOcean, or standard shared hosting.
The Bottom Line
A security widget that only exists in the browser is like installing a deadbolt on your front door but leaving the frame unattached to the wall. It looks sturdy from the sidewalk, but anyone who pushes against it will walk right through.
Taking ten minutes to audit your backend controllers—or letting an AI coding assistant run through your repository with tools like Turnstile Spin—will finally put an end to the mystery of why automated bots keep getting through your forms.
Master Architecture: Web perimeter security and automated scraper defense are detailed in our 2026 AI Software Engineering Playbook, highlighting behavioral telemetry against headless browser agents.